

This tutorial is helpful to verify that you are using correct Private key, or Certificate. You may face an issue when your certificate does not match to the private key and throws an error.
Method 1: Using OpenSSL and MD5
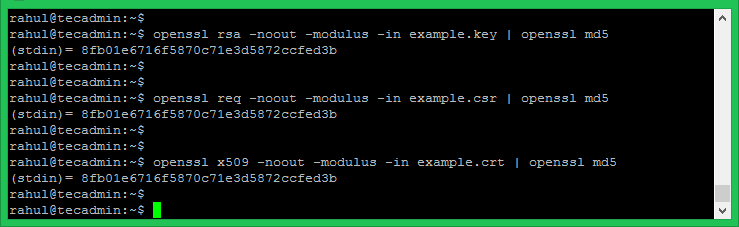
In the first method, The md5 value of certificate, key, and CSR should be same for all to work properly. If any of md5 is different means that file doesn’t relate to others.
$ openssl rsa -noout -modulus -in example.key | openssl md5
$ openssl req -noout -modulus -in example.csr | openssl md5
$ openssl x509 -noout -modulus -in example.crt | openssl md5
For example, check the md5 values are same for all the keys. It means they are related to each other and work properly.
Method 2: Using Openssl and sha256sum
Second method check for the SHA sum values of all files and check if the value of all files are same.
$ openssl pkey -in example.key -pubout -outform pem | sha256sum
$ openssl x509 -in example.crt -pubkey -noout -outform pem | sha256sum
$ openssl req -in example.csr -pubkey -noout -outform pem | sha256sum
For example, check the sha2 sum values are same for all the keys. It means they are related to each other and work properly.

How did it make you feel?




Thanks, this saved me a load of time setting up TLS on the althttpd server.
god bless you
good article mate it saved time for me thanks
you rock